AI in GxP Compliance: Human Oversight & Audit Trails
Learn how AI in GxP compliance combines human oversight, audit trails, and continuous validation to improve data integrity and inspection readiness in pharma.
1.0. Introduction
Why Human-in-the-Loop AI, audit trails, and continuous validation are becoming essential to accountable automation in life sciences.
An AI system generates a validation test script, flags a temperature excursion, and drafts an audit finding all in the same afternoon.
Six months later, an FDA investigator asks a simple question: “Can you show me who reviewed these outputs, what evidence they considered, and why the final decisions were made?”
The validation documents are available. The monitoring reports look complete. The audit findings have been approved.
But can your organization reconstruct the decisions behind them?
This is where the promise of AI in GxP compliance encounters an uncomfortable reality. Producing an accurate output is not the same as demonstrating a controlled process.
In pharmaceutical and biotechnology operations, decisions can affect product quality, patient safety, and regulatory compliance. Organizations therefore need more than intelligent systems that work efficiently. They need evidence that those systems operate under appropriate oversight.
Two principles make that possible, Human-in-the-Loop (HITL) governance and end-to-end audit trails.
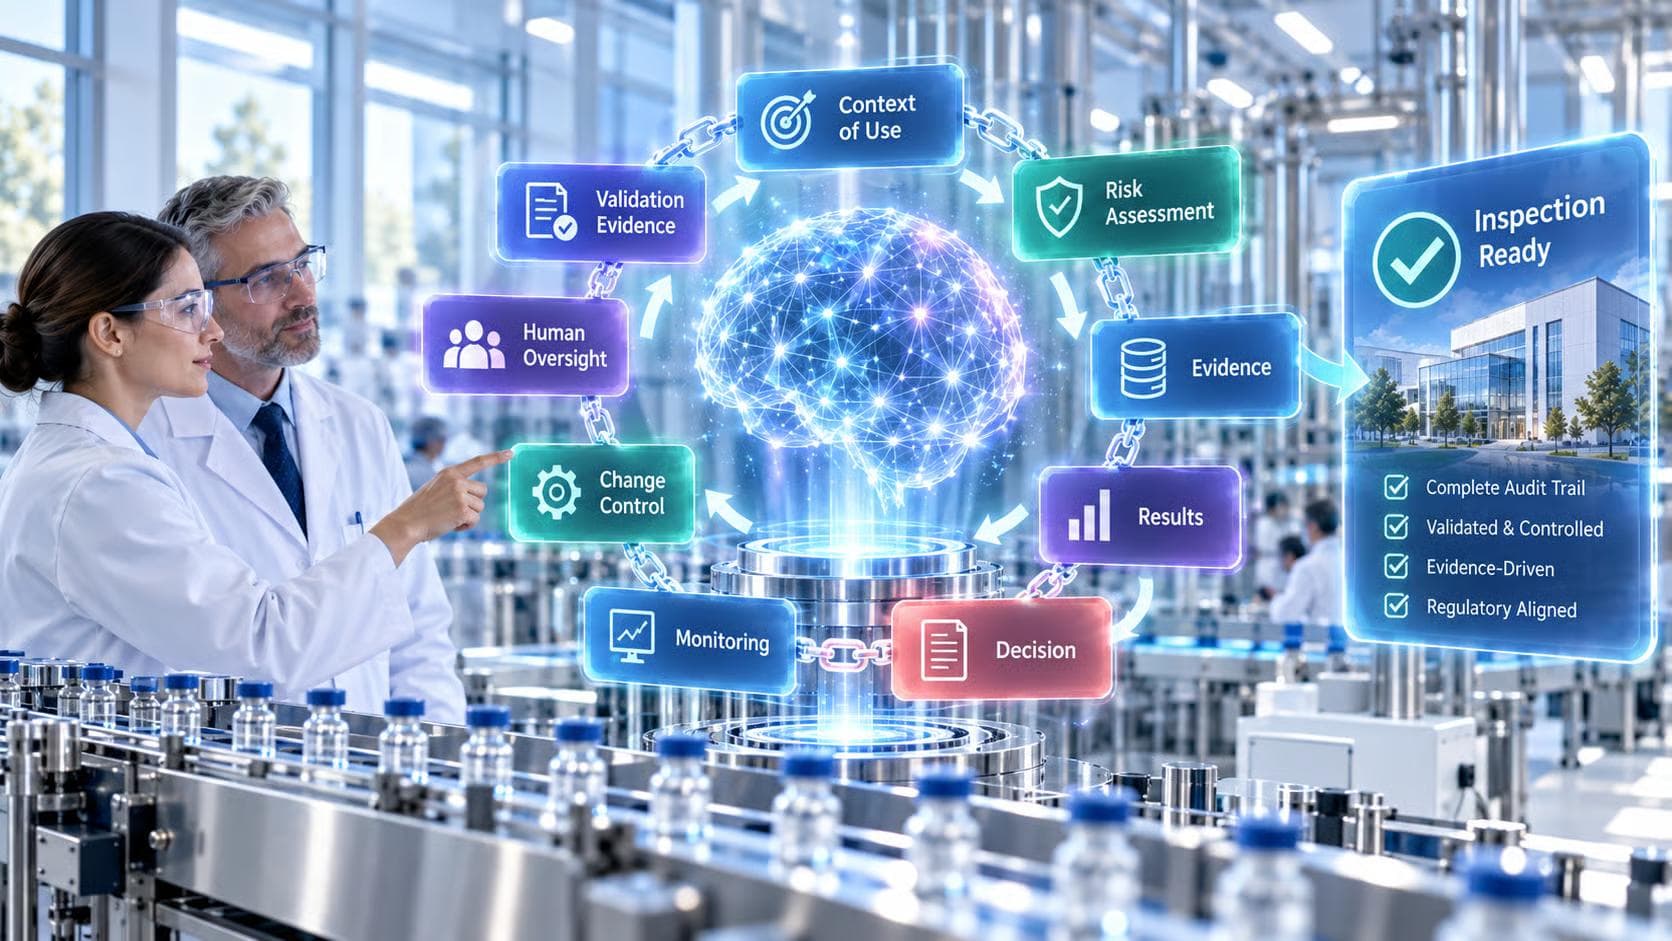
Together, they provide the foundation for a broader shift from documenting compliance at defined milestones to maintaining continuous, accountable assurance throughout the system lifecycle.
2.0. Why Human-in-the-Loop AI Matters in GxP
Imagine a validation team using AI to generate test scripts from a User Requirements Specification (URS).
The system produces a comprehensive-looking test package and reports that 80% of requirements have been covered. The remaining requirements are identified for additional review.
During that review, a validation specialist notices something important: a critical alarm function has no test for an unusual but credible failure condition.
The AI generated the expected operating scenarios. It missed the edge case that could reveal a significant control weakness.
This hypothetical example highlights a central limitation of AI-assisted validation. An output can appear technically complete while still requiring expert interpretation.
Human-in-the-Loop (HITL) means placing qualified professionals at defined decision points where they can evaluate, challenge, correct, or reject automated outputs before consequential approval.
The specialist identifies the missing scenario, documents the concern, and requests an additional test. The revised script undergoes review before becoming part of the approved validation package.
The system has accelerated preparation. The human has strengthened the outcome.
AI assists with analysis and execution. Human experts exercise judgment and retain decision authority.
This distinction is particularly important in regulated environments because automation does not transfer regulatory responsibility.
The regulated organization remains accountable for defining intended use, determining acceptable risks, validating computerized systems, and ensuring that appropriate personnel authorize quality decisions.
Human oversight must therefore be more than a final approval click. Reviewers need access to source requirements, generated outputs, identified gaps, and the rationale behind proposed changes.
But how does an organization prove that this review actually happened? That leads to the next critical requirement.
3.0. Why GxP Audit Trails Are Critical for AI-Powered Systems
Consider another scenario.
An automated temperature monitoring system detects an excursion in a pharmaceutical storage area. A quality professional investigates the event, evaluates the potential impact, documents the findings, and approves the response.
Months later, an investigator examines the event.
The organization must show what happened, when it happened, who was involved, what changed, and why the final decision was made.
A completed investigation report may summarize the outcome. But the report alone might not demonstrate the entire sequence of events.
This is the purpose of a GxP audit trail, to preserve a reliable, attributable history that allows organizations to reconstruct significant activities involving electronic records.
FDA 21 CFR Part 11 §11.10(e) requires secure, computer-generated, time-stamped audit trails for covered closed systems to independently record the date and time of operator entries and actions that create, modify, or delete electronic records.
EU GMP Annex 11 also addresses audit trails, including consideration of system-generated records of GxP-relevant changes and deletions, with reasons documented where appropriate.
These requirements establish an important regulatory foundation. When AI contributes to a regulated workflow, organizations should extend their traceability controls to relevant AI-generated recommendations and human review actions.
A system that produces an accurate result but cannot explain or reconstruct the process behind it still creates significant data-integrity and compliance risk.
Return to the validation example. The AI reports 80% requirements coverage. The reviewer discovers the missing alarm scenario and requests a correction.
A defensible record should preserve the original URS, the initial AI-generated script, the missing requirement identified by the reviewer, the reviewer’s identity, the reason for the correction, the revised test, and the subsequent approval.
The original output should not simply disappear when the corrected version replaces it.
This is what makes a human override defensible: preserving not just the final answer, but the evidence explaining how that answer changed.
The same principle strengthens inspection readiness.
When an investigator asks how the organization knew an AI-assisted decision was sound, a complete history connecting source data, AI output, reviewer identity, documented rationale, and authorization provides a much stronger answer than a standalone validation report.
An audit trail is not just a technical log. It is the connection between automation and accountability.
4.0. Continuous Validation: Moving Beyond Point-in-Time Compliance
Now consider what happens after a system successfully completes validation.
Requirements have been approved. Tests have passed. Deviations have been addressed. The validation report has been signed.
Three months later, a configuration changes. An integration is updated. An AI model begins producing different recommendations under changing operating conditions.
Is the original validation package still sufficient to support the system’s current intended use?
Not necessarily.
Traditional Computerized System Validation (CSV) often concentrates evidence around defined lifecycle milestones. Those milestones remain essential, but they do not eliminate the need to evaluate subsequent changes.
Continuous Validation is an ongoing, risk-based approach that connects system monitoring, change assessment, testing, evidence collection, and revalidation decisions throughout the operational lifecycle.
It does not mean repeating every validation test continuously.
Instead, organizations identify changes that could affect intended use or controlled operation, evaluate their significance, and determine what additional verification is necessary.
For AI-enabled systems, those changes may involve configurations, data inputs, integrations, or model performance even when the application appears unchanged to its users.
Continuous validation does not mean replacing quality systems with automation. It means strengthening existing controls through better connectivity between automated activities, human review, and controlled evidence.
This is where continuous assurance becomes meaningful. A system’s state of control should be supported by current, traceable evidence rather than relying exclusively on documentation produced at deployment.
And when circumstances change, organizations should have a clear path from detection to assessment, corrective action, human approval, and an updated validation state.
Want to learn more about xLM Continuous Intelligence?
5.0. How xLM Connects Human Oversight and Auditability Across Its Portfolio
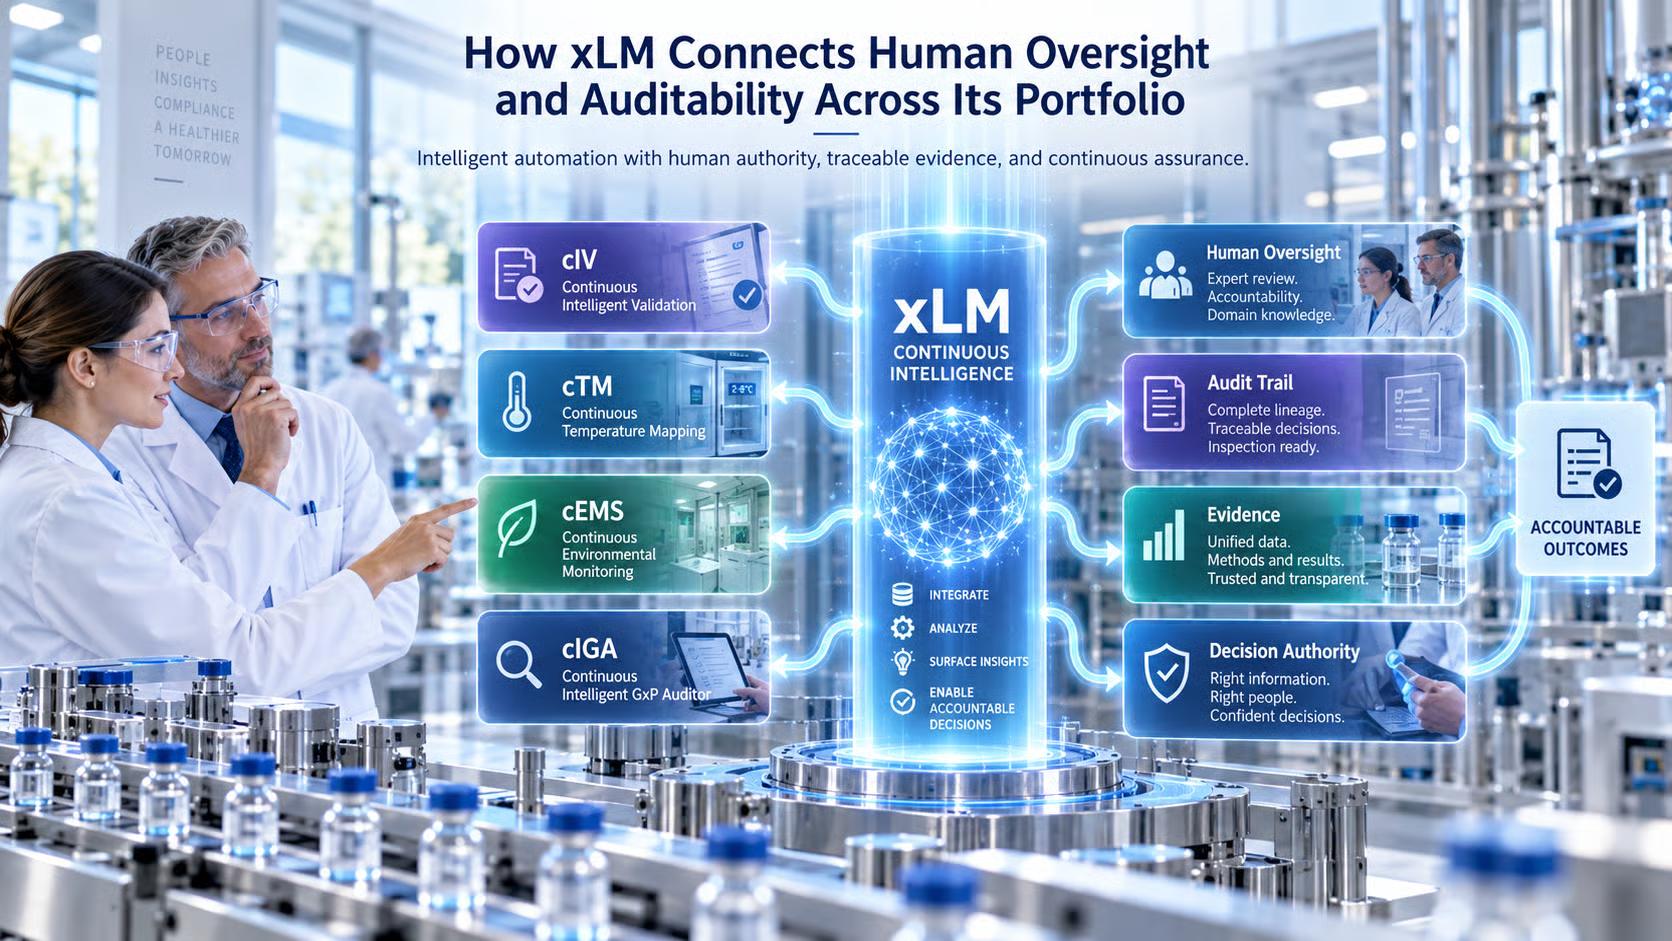
At xLM Continuous Intelligence, we are applying this philosophy across validation, monitoring, and auditing not as separate ideas, but as connected approaches to accountable automation.
Consider Continuous Intelligent Validation (cIV).
AI-assisted documentation and test generation can reduce repetitive validation work. But test suitability, deviations, execution evidence, and approvals still require qualified human judgment.
cIV's evidence-centric approach connects requirements, risk, test execution, reviewer actions, and approvals, helping organizations maintain traceability as systems evolve.
The same philosophy extends to temperature monitoring.
With Continuous Temperature Mapping (cTM), connected sensors, continuous monitoring, analytics, and alerts help identify conditions requiring attention. When an excursion occurs, responsible personnel assess its significance and determine the appropriate response.
Electronic records and audit trails help preserve the measurements, actions, changes, and approvals associated with that event.
Environmental data faces a similar challenge.
Through Continuous Environmental Monitoring System (cEMS), xLM supports controlled environmental-data acquisition, monitoring, review, and record management. Access controls, traceable records, audit trails, and electronic-signature capabilities provide a foundation for accountable oversight.
Auditing brings its own version of this gap.
With Continuous Intelligent GxP Auditor (cIGA), AI can assist with audit-question generation, evidence assessment, and recommendations. But auditors must still evaluate the supporting information, resolve uncertainty, and authorize consequential findings.
Audit versioning, review history, evidence associations, and approval records help preserve the reasoning behind the outcome. Automate what can be reliably automated, preserve human authority over consequential decisions, and maintain the evidence required to demonstrate control.
Across cIV, cTM, cEMS, and cIGA, the objective remains consistent: intelligent systems accelerate work, qualified professionals maintain decision authority, and controlled records support traceability.
Technology provides the foundation. Organizations remain responsible for appropriate validation, procedures, training, configuration, and quality oversight.
6.0. From Requirements to Execution: How cIV Makes AI-Assisted Validation Traceable
Consider a validation team preparing a User Requirements Specification (URS) for a GxP computerized system.
Using xLM's Continuous Intelligent Validation (cIV), AI can assist in generating requirements from approved source documentation, connecting generated statements to supporting references and making coverage information available for review.
Instead of treating the generated URS as a finished document, validation specialists can examine the source citations, requirement traceability, and coverage gaps as the documentation develops. They can identify unsupported requirements, correct inaccuracies, and approve the content through controlled review steps.
The same principle applies during Test Protocol Execution (TPE).
As tests are executed, cIV supports the capture of execution results and supporting evidence. Requirements coverage and traceability can be evaluated against the recorded outcomes, helping reviewers identify failed steps, missing evidence, and areas requiring investigation.
A failed test does not automatically become an accepted conclusion. Qualified personnel review the execution evidence, assess deviations, determine the appropriate action, and authorize the outcome.
Across both workflows, the objective is to maintain a connected record of what the AI generated, which sources supported it, what was executed, what changed, who reviewed it, and what was ultimately approved.
AI can generate requirements and execute tests, but human review and traceable evidence turn those activities into defensible validation records.
Importantly, FDA 21 CFR Part 11 and EU GMP Annex 11 do not categorically prohibit AI-assisted validation. Organizations can use automated tools within existing regulatory frameworks, provided applicable requirements for system validation, electronic records, audit trails, access controls, and authorized approvals are satisfied.
The use of AI does not remove these responsibilities.
By connecting AI-assisted URS generation, test execution, human-in-the-loop approvals, and maintained audit trails, cIV illustrates how intelligent automation can support a continuously reviewable validation lifecycle.
The real advancement is not simply generating validation evidence faster. It is making that evidence easier to trace, review, challenge, and defend during regulatory inspection.
7.0. The Future of AI in GxP Is Accountable Automation
The next stage of AI adoption in life sciences should not be measured solely by how many documents are generated or how many processes become automated.
The more important question is whether those efficiencies strengthen or weaken the organization's ability to demonstrate control.
Can the original information be retrieved? Can an AI-generated recommendation be distinguished from an approved decision? Can reviewers reconstruct the history of a change, including who made it and why?
These questions should influence how organizations evaluate AI validation, data integrity, and GxP compliance.
xLM’s vision is not to replace human expertise with AI, but to strengthen it with continuous access to reliable information, structured workflows, and traceable evidence.
The strongest implementations will connect automation with oversight throughout the lifecycle not merely add a signature to the end of an automated process.
That is the difference between using AI to complete tasks and using AI responsibly within a regulated quality system.
8.0. From Intelligent Automation to Continuous Assurance
For life-sciences organizations, the opportunity is significant: faster validation activities, better monitoring visibility, more efficient audits, and stronger connections between evidence and decisions.
But those benefits become sustainable only when human accountability and auditability are designed into the workflow.
At xLM, our cIV, cTM, cEMS, and cIGA platforms reflect this direction, supporting intelligent automation alongside controlled records, human review, and continuous assurance.
Want to learn how xLM builds trust in AI?
About the Authors
About Nagesh Nama
Nagesh Nama is the Founder and CEO of xLM Continuous Intelligence and ValiMation, bringing nearly 30 years of experience in AI-driven GxP compliance, computer system validation, and regulatory technology for the life sciences industry. A recognized thought leader, he pioneered the industry's first Continuous Validation platform supporting compliant IaaS, PaaS, and SaaS environments under 21 CFR Part 11 and Annex 11. His work focuses on advancing intelligent validation, AI-powered compliance, predictive maintenance, temperature mapping, and GxP AI agents to help pharmaceutical, biotechnology, and medical device organizations accelerate digital transformation while maintaining continuous compliance. Nagesh is a member of the Forbes Technology Council and the Fast Company Executive Board, a contributor to Forbes and Fast Company, and has been featured by Microsoft for his work in AI agents.